
Summary
- Binance founder Changpeng Zhao raised concerns about unnecessary identification data storage following Japan’s regulatory warning over sensitive customer information.
- Park24’s cybersecurity breach affected 6.63 million customer accounts, with attackers transferring over 1.46 million encrypted identification images to external destinations.
- Japan’s warning highlights data retention risks, raising concerns about how cryptocurrency exchanges protect sensitive customer information collected through KYC procedures.
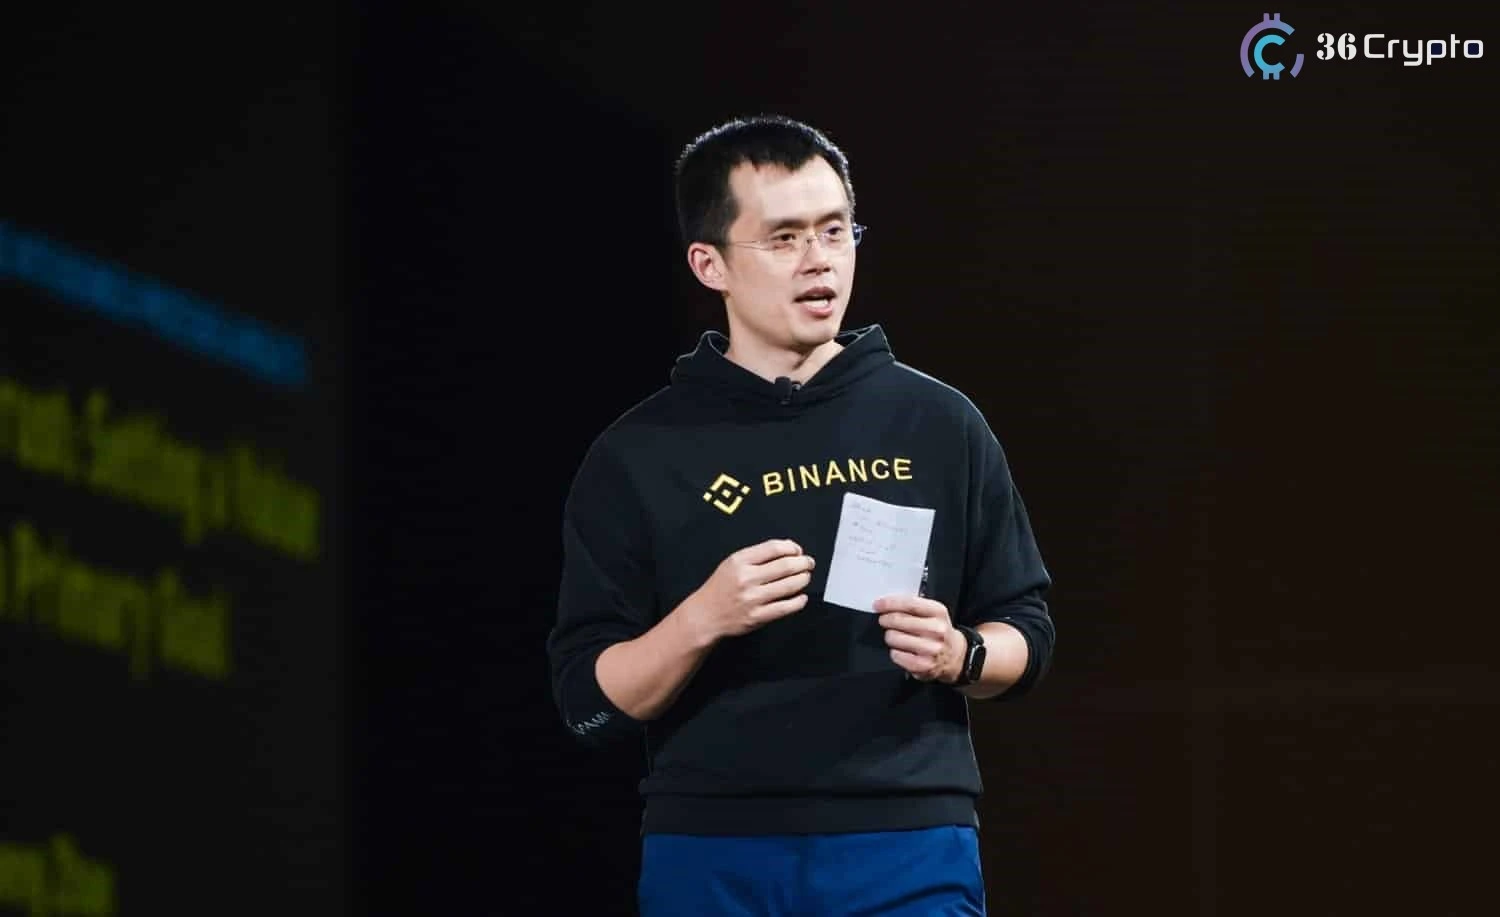
Binance founder Changpeng Zhao (CZ) has raised concerns about storing sensitive identification documents following a major cybersecurity breach in Japan. His remarks follow regulatory guidance urging businesses to limit unnecessary retention of customers’ personal information.
According to Changpeng Zhao (CZ), Japan’s Personal Information Protection Commission (PPC) warned companies against retaining identification images unnecessarily. The warning follows a cyberattack that compromised millions of customer records at a Japanese car-sharing service.
Also Read: Cardano Stablecoin DJED Announces Shutdown as December 31 Redemption Deadline Approaches
Japan’s Massive Car-Sharing Data Breach Exposes Millions of Customer Records
Japanese transportation company Park24 Group disclosed a major cybersecurity incident involving its Times Car service in October. The company detected suspicious activity on September 25 and investigated potential unauthorized access to customer information.
According to Park24’s October 23 disclosure, approximately 6.63 million customer accounts were affected by the security breach. Investigators discovered that attackers transferred 1,464,800 encrypted identification images, including driver’s licenses, to external destinations.
We're back on X.
— 36Crypto (@36Crypto1) August 21, 2026
Our previous account (36crypto2) is currently unavailable while we continue working through the appeal process. In the meantime, this is our new official account. While you are on this page, please support us by sharing and following.
Additionally, another 891,602 encrypted identification images experienced suspicious access during the incident. Investigators found no evidence that attackers transferred these additional documents outside the company’s systems.
Following the incident, Japan’s PPC issued guidance on November 18 addressing unnecessary storage of customer identification records. The regulator urged rental car companies to review their data retention practices and delete identification images when no longer necessary.
CZ’s Warning Raises Concerns Over KYC Data Storage at Crypto Exchanges
CZ’s reaction has brought broader concerns about personal information storage into the cryptocurrency industry’s data security conversation. Centralized cryptocurrency exchanges generally require customers to complete Know Your Customer (KYC) procedures before accessing trading services. These verification processes often involve submitting passports, national identification cards, driver’s licenses, and other sensitive personal documents.
Such information can expose customers to identity theft, phishing attacks, and fraudulent registrations if cybercriminals obtain unauthorized access. Significantly, Japan’s regulatory warning addresses unnecessary data retention rather than legitimate identity verification requirements.
Cryptocurrency exchanges must also comply with applicable regulations governing customer identification and record retention. Japan’s guidance specifically targets rental car businesses, highlighting the security implications of retaining identification documents beyond their intended purpose.
Also Read: XRP Could Explode to $8.89 as Analyst Reveals Critical Level Bulls Must Defend
